Open Source OpenClaw Alternatives
A curated collection of the 9 best open source alternatives to OpenClaw.
The best open source alternative to OpenClaw is Hermes Agent. If that doesn't suit you, we've compiled a ranked list of other open source OpenClaw alternatives to help you find a suitable replacement. Other interesting open source alternatives to OpenClaw are: nanobot, NanoClaw, ZeroClaw, and Eigent.
OpenClaw alternatives are mainly AI Personal Assistants but may also be AI Agent Platforms. Browse these if you want a narrower list of alternatives or looking for a specific functionality of OpenClaw.

Written by Piotr Kulpinski
Cross-platform desktop agent from Nous Research that connects to Telegram, Discord, Slack, WhatsApp, and more, with persistent memory, scheduling, and isolated sandboxing.
Hermes Agent is a desktop AI agent built by Nous Research that runs natively on macOS, Windows, and Linux. It's designed for people who want a single agent that works across their communication tools, handles recurring tasks, and actually remembers what it's done before.
The core idea is persistence. Most agents start fresh every session. Hermes maintains memory across conversations, auto-generates skills from past interactions, and builds up context about your projects over time. You don't have to re-explain things.
Where it connects:
- Telegram, Discord, Slack, WhatsApp, Signal, and email are all supported natively, so the agent meets you where you already work
- A CLI interface is also available for terminal-first workflows
What it can do:
- Natural-language scheduling for reports, backups, and briefings that run unattended
- Web search and browser automation with vision, image generation, and text-to-speech
- Subagents that run in isolated conversations with their own terminals and Python RPC scripts, useful for parallel pipelines without ballooning context costs
- Multi-model reasoning with access to 300+ models through the Nous Portal
Sandboxing is a genuine differentiator. Five execution backends (local, Docker, SSH, Singularity, and Modal) give you control over where code actually runs, with container hardening and namespace isolation. That matters if you're running automated tasks or untrusted scripts.
For teams or individuals already using LobeChat or similar multi-surface chat interfaces, Hermes takes a different angle: it's less about chat UI and more about an agent that operates autonomously across surfaces. Think of it as closer to an AgentOS approach, where the agent itself is the persistent layer.
It's free to use under the MIT license, with paid tiers through the Nous Portal for higher model access and monthly credits.
Lightweight, self-hosted AI agent that runs in a web UI, terminal, or chat app, handling long-running workflows with controlled token budgets.
nanobot is a minimal, self-hosted AI agent designed to run wherever you work: a web UI, your terminal, or a chat interface. It's built for people who want a personal AI agent they control, without the overhead of bloated frameworks or cloud-locked platforms.
The core design philosophy is lean execution. Rather than consuming tokens without restraint, nanobot applies sensible context management and explicit token budgets, so your costs stay predictable. That matters especially for long-horizon tasks, where the agent needs to sustain coherent reasoning across tens or even hundreds of steps without losing the thread.
Key capabilities:
- Multi-surface operation: runs in a browser-based web UI, a terminal, or directly inside chat apps, so you're not locked into one interface
- Long-running workflows: maintains steady execution across complex, multi-step tasks without context drift
- Token budgeting: built-in controls keep spending predictable, unlike agents that leave cost management entirely to the user
- Embeddable runtime kernel: the agent core is portable, so you can drop it into a business workflow or a personal automation setup without rewiring everything around it
- Self-hosted: your data stays on your infrastructure; no third-party service holds your conversations or task history
Compared to heavier agent frameworks or fully managed platforms like Agenta, nanobot stays deliberately small. The codebase is compact, the runtime is portable, and the architecture doesn't assume you want a full orchestration platform. It suits developers and technically minded individuals who want an agent they can embed, extend, or just run locally without a lot of ceremony.
It supports automation tasks, developer integrations, and conversational use cases through the same core runtime. The MIT license means you can adapt it freely for personal or commercial use.
Self-hosted AI agent that connects to WhatsApp, Telegram, Slack, and a dozen more messaging apps, running each agent in an isolated Docker container with credential injection via a secure vault.
NanoClaw is a self-hosted personal AI agent built for individuals who want full control over their AI assistant. It connects to messaging apps including WhatsApp, Telegram, Discord, Slack, Microsoft Teams, iMessage, Matrix, Google Chat, Webex, WeChat, and email, then routes every conversation through isolated Docker containers. The codebase is intentionally small: 132 source files, roughly 17,500 lines of code, and fewer than 10 dependencies. You can read the whole thing in an afternoon.
It positions itself as a lightweight alternative to OpenClaw, which ships 3,680 source files and 70 dependencies. That size difference isn't cosmetic. It shapes whether you can audit what your agent actually does, customize it without fear, and trust its security model.
Security is structural, not policy-based. Each agent group runs in its own Linux container with its own filesystem. It can only see directories you explicitly mount. Credentials never enter the container at all. Outbound API requests route through OneCLI's Agent Vault, which injects authentication at the proxy level and enforces per-agent rate limits and policies.
Key capabilities:
- Multi-channel messaging – WhatsApp, Telegram, Slack, Discord, Teams, iMessage, Matrix, and more, installed on demand with
/add-<channel>skills - Flexible agent wiring – give each channel its own isolated agent, share one agent across channels for unified memory, or fold channels into a shared session
- Per-agent workspaces – each agent group has its own memory, its own
CLAUDE.md, and its own container boundary - Scheduled tasks – recurring jobs that run Claude and message you back (morning briefings, weekly reviews)
- Multiple AI providers – runs Claude Code natively via the Claude Agent SDK; drop-in options for OpenAI Codex, OpenRouter, Google, DeepSeek, and local models via Ollama
- Skills over features – install only the adapters you need; nothing is bundled that you didn't ask for
The architecture is a single Node.js host process that routes inbound messages through an entity model, writes to SQLite, and wakes per-session containers. No microservices, no message brokers, no shared memory across agent boundaries.
NanoClaw is MIT-licensed and designed to be forked. The philosophy is that your personal AI agent should be working software shaped to your exact needs, not a generic framework you configure around.
A single Rust binary that runs a personal AI agent on your own hardware, connecting to 70+ LLM providers and 30+ messaging channels with built-in sandboxing and cryptographic tool receipts.
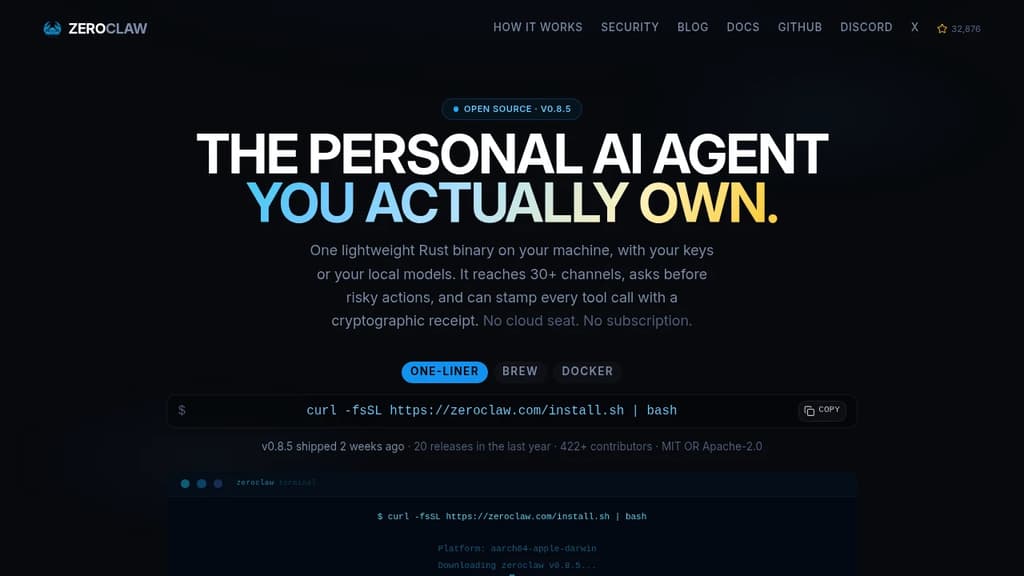
Most AI assistants are a seat you rent on someone else's infrastructure. ZeroClaw runs as a single native binary on your own machine, using your own API keys or fully local models like Ollama. No cloud seat, no subscription, no ZeroClaw server in the middle.
The binary is built in Rust and starts in under 20ms. It uses less memory than a browser tab and runs on everything from a workstation to a Raspberry Pi, including ARM and x86. There's no Node, JVM, or Python environment to install.
What it connects to:
- 70+ LLM providers: local options like LM Studio, llama.cpp, vLLM, and LocalAI, plus hosted providers including Anthropic, OpenAI, Google Gemini, Amazon Bedrock, Mistral, Groq, and any OpenAI-compatible endpoint
- 30+ channels: Telegram, Discord, WhatsApp, Slack, Signal, iMessage, Matrix, email, IRC, Bluesky, Reddit, Nostr, Notion, webhooks, and more
- Hardware: GPIO on Raspberry Pi, STM32, Arduino, and ESP32
Security is the default posture, not an add-on.
- Supervised autonomy: medium-risk actions require your approval before they run; high-risk ones are blocked outright
- OS-level sandboxes: Landlock, Bubblewrap, Seatbelt, or Docker contain what the agent can touch, enforced by the kernel rather than a prompt
- Command allowlists: explicit workspace scoping decides what runs and where
- Tool receipts: every successful tool call can be stamped with an HMAC-SHA256 tag the model cannot forge, making fabricated runs or invented results detectable
YOLO mode exists for trusted dev environments and is strictly opt-in.
The agent supports multiple named agents running from a single daemon, each isolated. Skills package repeatable tasks with their tools. Scheduled jobs, webhook triggers, and channel events all run through the same agent loop inside the same sandbox and allowlists you've scoped. A2A discovery lets agents describe and find one another through the gateway.
With a local model, nothing leaves your machine at all. With a hosted provider, only your prompts go to the provider you chose, using your own key. Dual-licensed MIT OR Apache-2.0.
Self-hostable desktop app that runs a coordinated team of AI agents to browse the web, manage files, execute terminal commands, and complete complex workflows.
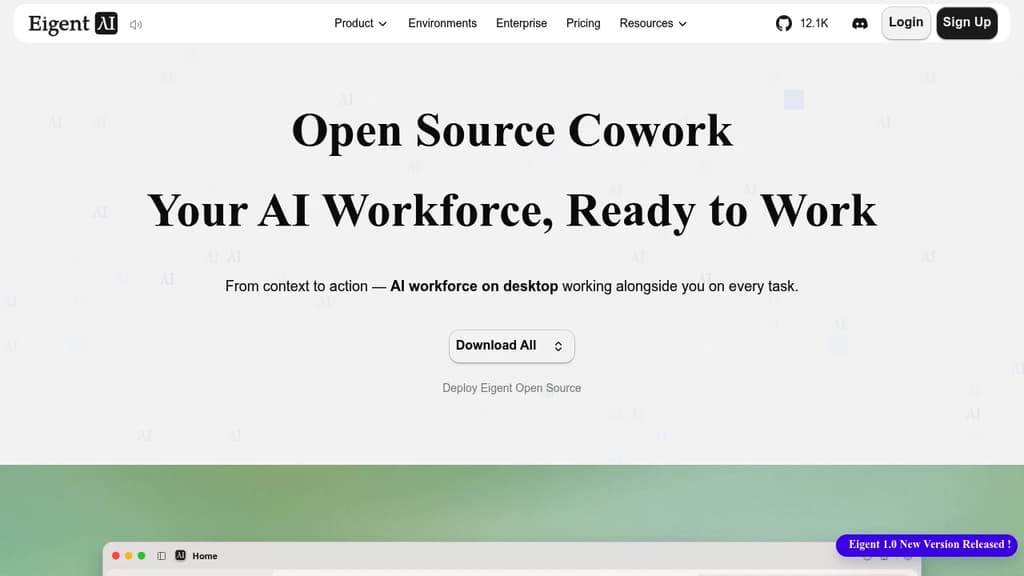
Eigent is a desktop application that puts a multi-agent AI workforce on your machine. You describe a task, and a pool of specialized agents divides it up, works in parallel, and delivers results. It's built for people who want AI to actually finish work, not just assist with it.
The core idea is "cowork": agents operate alongside you in your desktop environment with access to your local files, browser, and terminal. You can run a single focused agent for direct tasks or spin up a full workforce where agents collaborate across steps. A Browser Agent handles web research, a Document Agent reads and writes files, a Terminal Agent runs shell commands, and a Multi-modal Agent processes images and other media.
Key capabilities include:
- Scheduled automation: set recurring workflows so agents run tasks on a timer, even when you're not at your desk
- Local-first execution: files, credentials, and context stay on your machine; nothing has to leave it
- Model agnostic: connect cloud APIs, enterprise model gateways, or local inference. No vendor lock-in
- MCP and skill support: track which tools, skills, and referenced files each agent uses during a task
- Agent folder: every file an agent creates or modifies during a task is surfaced in one place for review
The open source version is fully self-hostable with your own API keys or local models. It's built on CAMEL-AI, a multi-agent framework, and runs on Mac, Windows, and Linux.
For teams doing research-heavy work, competitive analysis, report generation, or any task that involves pulling from multiple sources and producing structured output, Eigent is closer to OpenHands than a simple chat interface. It's designed to complete multi-step work end-to-end rather than hand control back to you at every turn.
Runs AI agents inside Trusted Execution Environments on NEAR AI Cloud, keeping credentials encrypted and invisible to the model at all times.
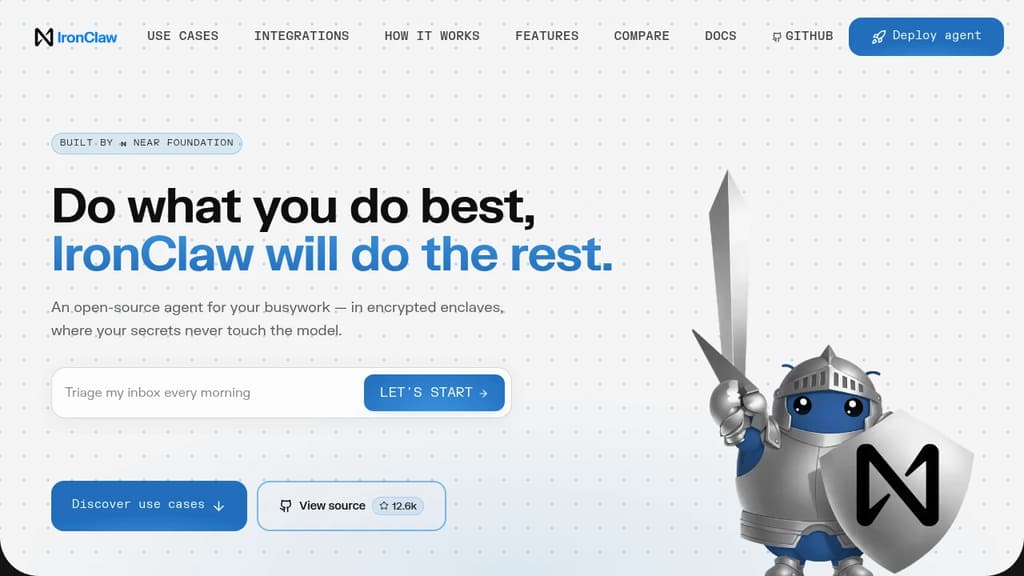
IronClaw is a secure AI agent runtime built for people who want to hand off real work to an AI agent without handing over their passwords, API keys, and tokens along with it. It runs on NEAR AI Cloud inside Trusted Execution Environments, meaning credentials are encrypted in memory from boot to shutdown. The AI model never sees the raw values.
The core problem it solves is real. Tools like OpenClaw give agents broad system access, but that access cuts both ways. A crafted prompt can trick the model into leaking every secret it holds. Malicious community skills have been found specifically designed to exfiltrate credentials. IronClaw's answer isn't a policy or a warning prompt; it's architecture.
Key security layers:
- Encrypted vault: Credentials are stored encrypted at rest and injected into outbound requests only at the host boundary, only for endpoints you've pre-approved.
- Per-tool Wasm sandboxes: Every skill runs in its own WebAssembly container with capability-based permissions. A compromised tool can't reach anything outside its sandbox.
- Network allowlisting: Tools can only contact endpoints you've explicitly approved. No silent phone-home, no unknown destinations.
- Real-time leak detection: Outbound traffic is scanned continuously. Anything resembling a secret heading out gets blocked before it leaves.
- Built in Rust: Memory safety is enforced at compile time. No garbage collector, no buffer overflows, no use-after-free vulnerabilities.
On the practical side, IronClaw handles the kind of recurring busywork that eats time. Inbox triage, daily briefings, meeting prep, deployment health checks, release tracking, invoice parsing, KPI reporting. It connects to Gmail, Google Calendar, Slack, Telegram, GitHub, Linear, Google Sheets, and anything else with an API. Missing an integration? It builds the connector itself from a plain-language description.
It's model-agnostic, compatible with Anthropic, OpenAI, Gemini, Mistral, Ollama, and several others. Deployment is one click on NEAR AI Cloud, with a free starter tier and paid plans scaling up to five concurrent agent instances.
Deploy AI agents inside your own infrastructure with document-grounded answers, computer use, and support for any AG-UI-compatible agent framework.
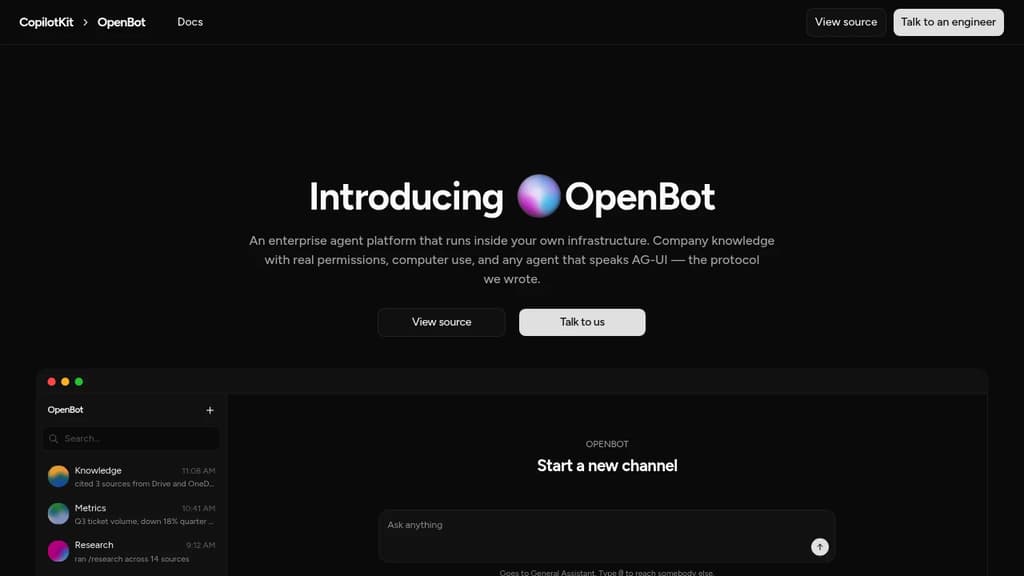
OpenBot is a self-hosted enterprise agent platform built for companies that can't afford to hand their data to a third party. It runs on your own infrastructure, keeps documents and conversations in your own Postgres database, and enforces the same file permissions your existing systems already have. Every agent gets its own channel, behaves like a named colleague, and only has access to the tools and sources its role requires.
The platform ships several agent archetypes out of the box:
- Knowledge agent answers questions from connected company documents (Google Drive, OneDrive) and always cites the source files, so answers can be verified rather than trusted.
- Metrics agent queries your analytics warehouse and draws the answer directly instead of describing it in prose.
- Research agent gathers context across documents and drafts from them, keeping contradictory sources rather than quietly picking one.
- Tool operator signs into interfaces that have no useful API and drives them the way a person would. You can watch the screen in real time and take control mid-task.
- Inbox triage, onboarding buddy, and other role-based agents can be published and scoped to exactly the skills they need.
Permissions are fail-closed throughout. An agent only sees files the person asking is already allowed to open. Documents with ambiguous permission mappings aren't returned at all. Sensitive tool calls go through a gateway with an explicit per-tool allowlist, and every call is logged.
OpenBot is built on AG-UI, the Agent-User Interaction Protocol that the team behind OpenBot wrote and maintains. This means any agent that speaks AG-UI, whether built on LangGraph, Mastra, PydanticAI, or a custom framework, can be registered as an endpoint and given a channel. No lock-in to a single agent framework.
On the infrastructure side: no shared tenancy, no seat counting, and no bundled model. Admins supply their own provider credentials, which are encrypted at rest and never logged. Nothing silently falls back to an external LLM if a provider isn't configured. Helm is the supported production deployment path.
Run a team of AI agents locally on your own API keys and subscriptions, with scheduled tasks, computer use, and Gmail, GitHub and Slack integrations.
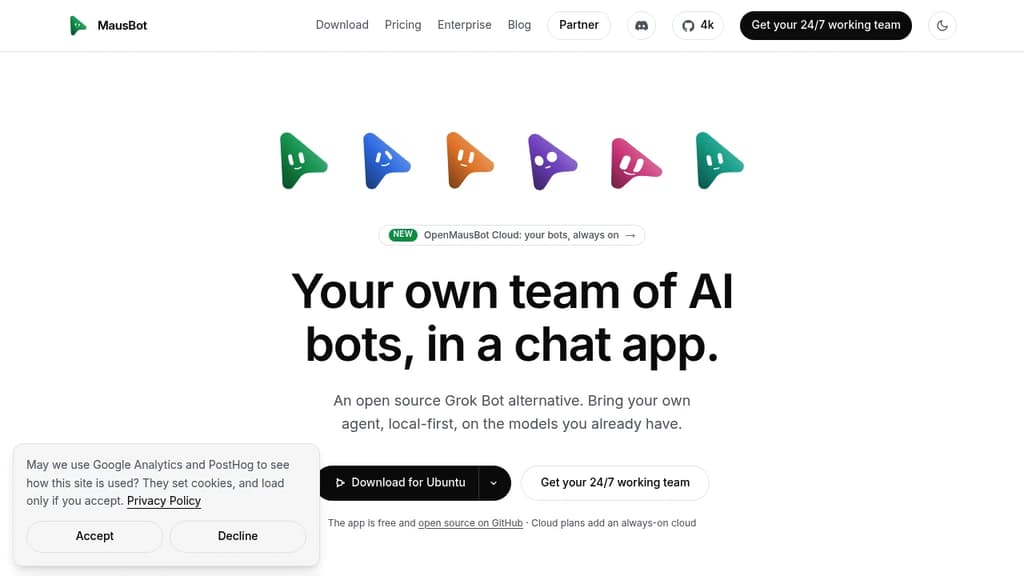
MausBot is a local-first Grok Bot alternative that lets you run a team of AI agents from a familiar chat interface. Each bot gets its own model, its own computer, and access to your connected apps. They work in parallel, come back when something needs your attention, and never proxy your credentials through a third party.
It runs on Mac, Windows, and Linux under Apache 2.0. Your transcripts, keys, and events stay in a local folder on your own disk. Local-first isn't a setting; it's the default.
Key capabilities:
- Model per bot. Assign Claude, Codex, or other models to individual bots and switch mid-conversation.
- Computer use. Each bot gets a desktop it can see and click, either a cloud desktop from a provider you connect or your local machine directly.
- Scheduled tasks. Inbox sweeps, weekly reports, competitor watches, PR reviews, and support triage all run on a calendar you define.
- Connected apps. Gmail, Slack, GitHub, Notion, Linear, and hundreds more via Composio. Authenticate once and every bot on the team can use them.
- Voice. Hit call and the bot hears you, narrates its work, and asks for approvals out loud.
- Playbooks. A whole team, its routines, and its app connections ship as a single Markdown file. Connections stay off until you approve them.
- Manage bots like contacts. Pin, duplicate, mark unread, hide, or delete. The interface is a messaging app, not a dashboard.
For teams that want bots running around the clock without leaving a laptop on, Cloud plans add always-on workspaces with scheduled tasks and voice included. You still bring your own Claude or ChatGPT account; MausBot never sits between you and the model provider.
Compared to other AI chat interfaces, MausBot is built specifically for multi-agent workflows where each agent has persistent tasks, tool access, and its own compute rather than just a shared conversation window.
Run persistent AI bots that sign into your tools, complete tasks autonomously, and ask for approval when needed. Your keys, your model, your infrastructure.
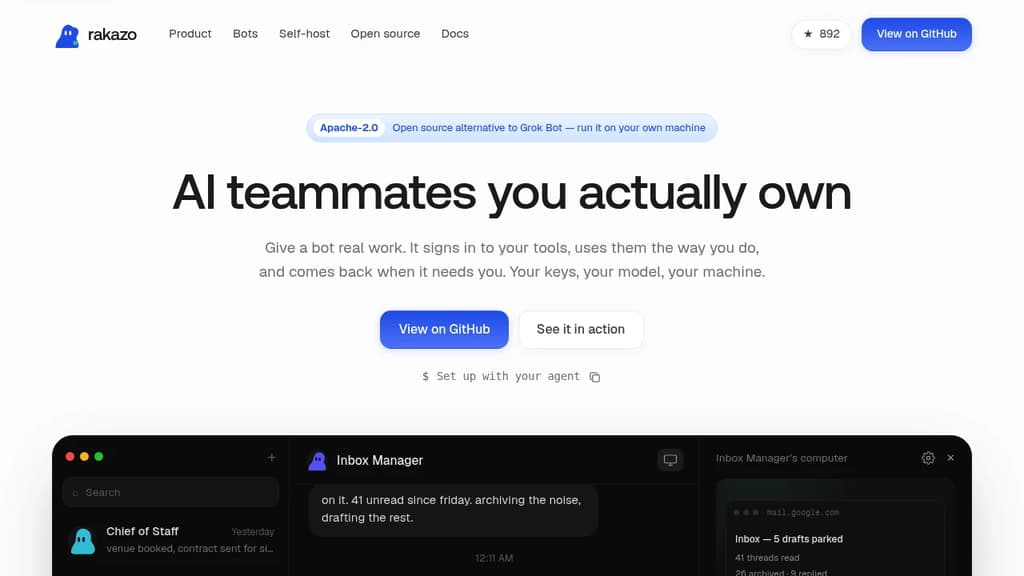
Rakazo is a self-hosted platform for running AI agents that actually do things. Each bot gets a sandboxed browser and shell, signs into your tools the way you would, and completes tasks while you're away. It's a direct Grok Bot alternative built around one principle: you own everything.
Bots run in Docker on your own machine, behind your firewall. Sessions and credentials never leave your infrastructure. You point each bot at whatever model you want (Claude, GPT, Grok, or a local model), and you can mix and match per bot. The cheap model triages; the smart one writes.
Setup starts with an interview. A new bot asks you a few questions about the work, your writing style, and which tools it should use. Then it gets going.
What bots can handle out of the box:
- Inbox Manager archives noise, replies to routine threads, and parks drafts for your review
- Sales Outbound researches accounts overnight, scores intent, and drafts outreach in your voice
- Talent Scout reads applicants, shortlists against your criteria, and writes intro emails
- Bug Triage reproduces reports in a real browser and attaches reproduction steps to the issue
- Expense Manager matches receipts to charges and files reports, asking before guessing
- Chief of Staff runs briefings, bookings, and handoffs between your other bots
Routines are saved as plain Markdown. Show a bot a workflow once and it writes a routine you can read, edit, and commit to version control. Approvals are configurable: set what a bot may do alone and what it must ask you about first. Every action lands in an audit log you own.
Rakazo is Apache-2.0 licensed with no seats, no pricing tiers, and nothing gated. Unlimited bots, no limits on usage. A managed cloud option (where you bring your own keys and they run the sandboxes) is planned, with no migration required when it arrives.

People are looking for alternatives to...
View all alternatives
Claude Code
Spotify
CapCut

Claude
Notion
Lovable
 Openlane – Open-source, developer-first platform for automated compliance, risk management, and built-in Trust Center.
 Bright Data